
Symbiosis Recovers 15 BTC After Bridge Exploit and Offers the Attacker a 20% Bounty
0
0
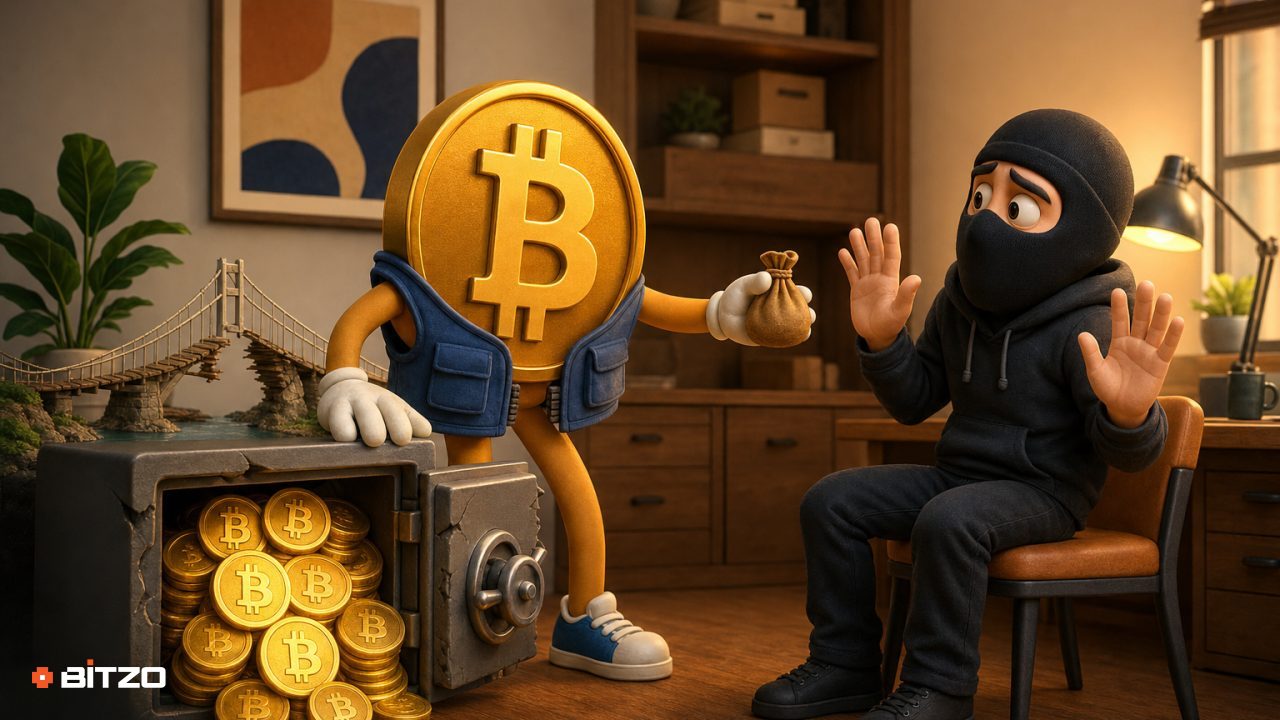
Symbiosis said it recovered approximately 15 BTC and moved the funds into a team-controlled multisignature wallet after an attacker exploited a vulnerability in its Bitcoin Bridge at about 04:28 UTC on September 11, 2026. The protocol suspended BTC-related routes following the incident, according to its official statement.
Independent on-chain monitoring cited by Lookonchain estimated roughly $336,000 in WBTC losses linked to abnormal syBTC minting; Symbiosis said its final loss calculation was still under way.
Bitcoin Bridge exploit triggers BTC route suspension
Symbiosis said it halted BTC-related routes after identifying its Bitcoin Bridge as the affected product. The company did not provide a technical account of the vulnerability or identify the attacker.
The operational impact was described as limited to that bridge: according to Lookonchain, EVM, TRON and TON routes, Octopools and other components remained operational and unaffected.
For users, the suspension covers BTC-related activity rather than every network and product supported by the cross-chain protocol. The available disclosures did not say when the halted BTC routes would resume.
15 BTC recovery sits alongside an unconfirmed loss estimate
Lookonchain attributed the reported loss estimate to independent monitoring that linked the incident to abnormal syBTC minting through Symbiosis BridgeV2. It put WBTC losses at approximately $336,000.
Separately, Symbiosis reported recovering roughly 15 BTC and placing it in a team-controlled multisignature wallet. The protocol has not disclosed further details about the custody setup.
The two figures should not be read as a completed accounting: Symbiosis said it was still calculating the final losses. The released information did not provide a breakdown of affected positions or recipients, and the recovery does not itself establish a final loss figure or completed restitution plan.
Symbiosis sets September 13 deadline for attacker bounty
Symbiosis has offered the attacker a 20% white-hat bounty in exchange for returning the stolen funds. The offer remains open through September 13, 2026, the protocol said in its September 11 statement.
After that deadline, Symbiosis said the same reward would instead be offered for information leading to the recovery of the funds. The announcement frames the proposal as a time-limited path for the attacker to return assets before the reward is redirected toward informants.
For now, the bounty shows only that a recovery effort remains outstanding. The protocol has not said whether it received a response to the offer or disclosed how or when a return would occur, so there is no evidence here that additional assets have been recovered.
Compensation framework remains under development for liquidity providers
The outstanding question for users is how the incident will be resolved for liquidity providers whose funds may have been exposed. PANews, in a September 12 report carried by KuCoin, said Symbiosis planned to contact affected liquidity providers and was developing a compensation framework.
Neither a final loss amount nor the terms of that framework had been confirmed at the time of the report. There is also no disclosed schedule for outreach, compensation calculations or distributions.
For now, Symbiosis has provided three concrete markers: BTC-related routes were suspended after the exploit, about 15 BTC was placed in a team-controlled multisignature wallet, and the attacker has until September 13 to accept the 20% return-for-bounty proposal. The eventual accounting and the compensation process remain pending.
Disclaimer: This article is provided for informational purposes only. It is not offered or intended to be used as legal, tax, investment, financial, or other advice.
0
0

 Gérez tous vos cryptos, NFT et DeFi à partir d'un seul endroit.
Connectez de manière sécurisée le portefeuille que vous utilisez pour commencer.


