DarkSword Exploit: Safari Visit Could Expose iPhone Crypto Wallets
0
0
DarkSword Exploit: 1inch Warns Safari Can Expose iPhone Wallets
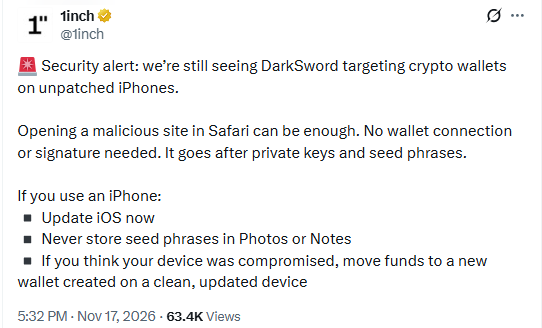
1inch warned on November 17 that DarkSword is still targeting crypto wallets on unpatched iPhones. Opening a malicious site in Safari can be enough. No wallet connection or signature is needed. This DarkSword exploit report separates the new warning from older research.
DarkSword is not new. Google documented it on March 18, 2026. The new development is the exchange aggregator saying attacks continue.
What 1inch Warned and What Is Confirmed
Statement | Source | Status |
Still targets unpatched iPhones | 1inch X, Nov 17 | Stated; no victim numbers |
A malicious Safari page can be enough | 1inch, Google research | Documented |
No connection or signature needed | 1inch | Stated |
Goes after keys and seed phrases | 1inch | Stated |
iOS 18.4 to 18.7 affected | Google, March 2026 | Documented; not in 1inch's post |
Google's Threat Intelligence Group found six chained vulnerabilities, several of them zero-days when used. It linked several actors to attacks since November 2025, including targets in Saudi Arabia, Turkey, Malaysia and Ukraine. Google reported the flaws to Apple in late 2025. The 1inch post is the primary source for the November 17 warning. Apple's own advisories remain the reference for patch details.
1inch is a transaction aggregator and wallet provider. Its post names no wallets, versions, victims or losses. Google named three malware families delivered after exploitation: GHOSTBLADE, GHOSTKNIFE and GHOSTSABER.
This is not a new zero-day. Opening a page is still a user action, so it is not zero-click either.
Which iPhones Are at Risk and What Did Apple Patch?
iOS branch | Documented fixes |
iOS 18 | Fixes in 18.6, 18.7.2 and 18.7.3; 1inch's summary cites 18.7.7 |
iOS 26 | Final fix in iOS 26.3 |
Google says all six flaws were patched by iOS 26.3, with most fixed earlier. CertiK reported a newer DarkSword version on November 6, still aimed at unpatched iPhones.
Apple's November 9 releases were iOS 27.2.1, plus 26.7.3 and 18.7.12 for devices that cannot run Apple's mobile operating system 27, per update coverage. Check Settings for the newest version. Apple's iOS 26.3 notes list a fix for CVE-2026-20700, one part of the chain. Patched devices are protected against the known chain. CertiK reportedly named MetaMask, Trust Wallet, Phantom, Exodus and Coinbase among targeted wallet apps.
DarkSword Exploit: How iPhone Crypto Users Should Protect Wallets
For any DarkSword exploit scare, speed matters. An exposed seed phrase must be abandoned, not just the app.
Update Apple's mobile operating system now, under Settings, General, Software Update
Never store seed phrases in Photos or Notes
Where updating is impossible, Google recommends Lockdown Mode
If you suspect compromise, create a new wallet on a clean, updated device and move funds
Consider a hardware wallet for large holdings, as CertiK advises
Updating does not recover funds already taken. It only closes the known entry route. Switching wallet apps may not help, because the attack targets the device. Avoid unknown links and ads on unpatched phones.
This is general guidance, not an instruction from Apple.
The Bottom Line
This DarkSword exploit warning concerns unpatched iPhones, not a new flaw. Update iOS, keep recovery phrases out of Photos and Notes, and treat any exposed seed phrase as lost.
YMYL Disclaimer: This article is for informational purposes only and is not financial or security advice. It is based on the exchange aggregator, Google, Apple and security-firm reports reviewed as of November 18, 2026. Victim numbers and losses remain unknown, and the latest iOS version may have changed. Follow official security guidance and verify current details before acting. No wrongdoing is alleged or implied. Crypto assets carry a risk of total loss.
0
0

 Manage all your crypto, NFT and DeFi from one place
Securely connect the portfolio you’re using to start.


