Chainflip Confirms $12M Hack, Offers 10% Bounty to Attacker
0
0
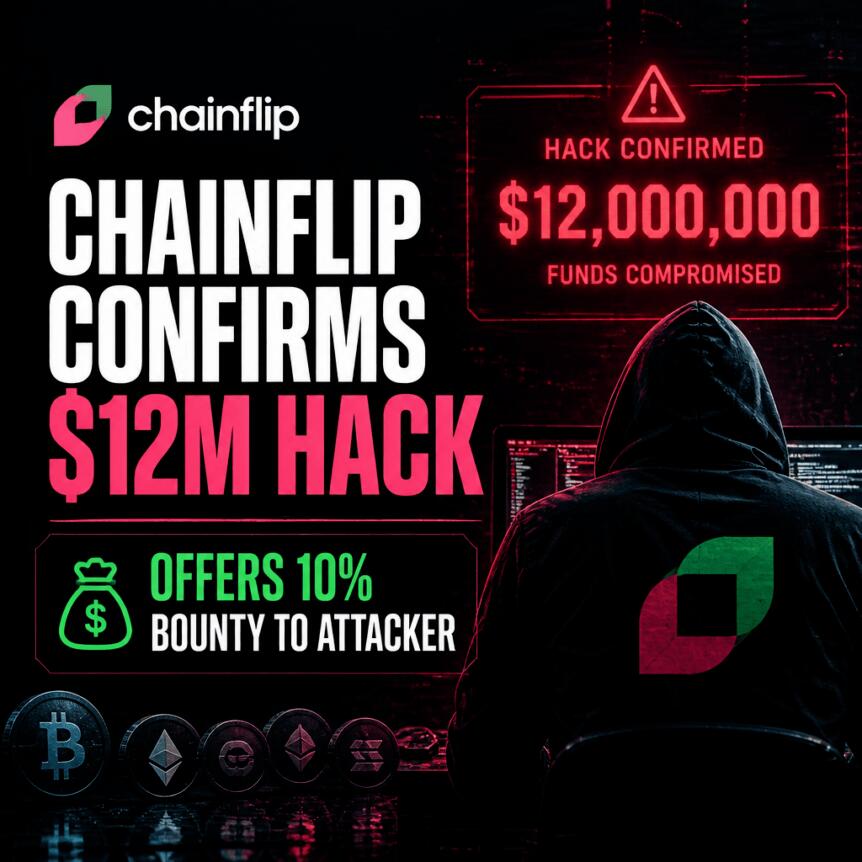
Cross-chain swap protocol Chainflip says an attacker stole roughly $12 million from its vaults on Saturday, marking a significant escalation from an earlier figure that put the loss at $4.86 million. The theft involved Bitcoin, Ether, and stablecoins, according to Chainflip Labs’ statement.
In an outreach addressed to the attacker, Chainflip Labs reported that 122.86 BTC, 520.22 ETH, 3.25 million USDC, and 758,141 USDT were taken. The company then set a deadline for the return of the remaining assets and tied the outcome to whether it would keep pursuing law-enforcement channels.
Key takeaways
- Chainflip expanded its incident estimate: the reported theft is now about $12 million, up from an earlier $4.86 million figure.
- Specific amounts were named: the attacker allegedly took 122.86 BTC, 520.22 ETH, 3.25 million USDC, and 758,141 USDT.
- A time-limited return offer was made: Chainflip offered a 10% bounty for returning the remaining 90% by 18:38 UTC on Nov. 23.
- The protocol is tracing possible funding and infrastructure: Chainflip linked preparations to Tornado Cash activity on Nov. 11 and a validator account registered on Friday.
- Token reaction was sharp: CoinGecko data cited by Chainflip’s statement shows FLIP fell 42.9% over the previous 24 hours.
Stolen assets and a return window
Chainflip Labs said it “confirmed” the Saturday theft, and it quantified the outflow from its vaults across four asset types. The company’s statement frames the incident as a specific compromise affecting pooled funds rather than a broader exploit affecting every component of the protocol.
To encourage a partial recovery, Chainflip offered what it characterized as a white-hat pathway: returning the remaining 90% of the stolen assets by 18:38 UTC on Nov. 23. If the deadline is met, Chainflip said it would withdraw its reports and complaints to law enforcement, treating the return as a legitimate recovery rather than an ongoing criminal act.
The stated structure is straightforward: an attacker who complies by the deadline would receive a 10% bounty, while the rest would be returned. The company also indicated that if the funds are returned in time, it would update its external reporting posture accordingly.
What Chainflip says it found about the attack
Chainflip’s account of how the compromise may have been executed points to pre-positioning rather than an opportunistic exploit discovered after the fact. The company said it traced preparations for the attack to Tornado Cash funding on Nov. 11 and to a validator account registered on Friday.
While the statement does not provide the full technical anatomy in a public, step-by-step way, it claims the team identified the “mechanism behind the cryptographic key exposure.” Chainflip added that it has taken steps to prevent similar attacks going forward.
The company also said it obtained identifying information connected to the attacker that could help authorities. In the message, Chainflip further asserted that it holds identifying data tied to the validator and the servers used, and that the attacker’s addresses are already “flagged across every major analytics firm.” It also claimed that every Tornado Cash withdrawal connected to the activity is being monitored.
Chainflip’s stance appears designed both to increase pressure on the attacker and to reinforce confidence that the protocol’s team can support follow-up investigations. For investors and users, the key issue is whether the protocol’s mitigation actions address the underlying exposure vector rather than only blocking a single replay or incident-specific pathway.
Why the protocol’s stability narrative is now under scrutiny
Cross-chain infrastructure depends heavily on assumptions about custody, key management, and validator operations. When those assumptions are challenged—especially via exposure of cryptographic keys—the incident can raise questions beyond the immediate losses: whether similar exposures could recur, whether other operational accounts were affected, and how thoroughly the system’s security model has been validated.
Chainflip’s statement indicates it has already identified the exposure mechanism and implemented preventative measures. Still, the public disclosure of specific stolen amounts and the involvement of Tornado Cash funding highlight a typical pattern seen in crypto theft: attackers often attempt to break attribution trails through mixer-like services before executing a compromise.
Market reaction suggests participants are evaluating Chainflip not only on the size of the theft, but also on how quickly and convincingly it can explain the breach and demonstrate that the same failure mode cannot be repeated. According to CoinGecko data referenced in the statement, Chainflip’s FLIP token dropped 42.9% over the prior 24 hours, underscoring how swiftly confidence can erode after security incidents in cross-chain systems.
That token move is also notable for its speed and magnitude: for traders, it implies the market was repricing the risk associated with Chainflip’s design and its operational security. For long-term stakeholders, the more important question is whether the mitigation steps address the same class of weakness—particularly around validator-related processes and key handling.
What to watch next as recovery efforts begin
Chainflip has provided a clear near-term milestone: the return offer expires at 18:38 UTC on Nov. 23. Over the coming days, the market will likely focus on whether any funds are moved back, whether the company releases additional technical detail about the exposure mechanism, and whether its prevention steps hold up under real-world operational conditions.
Even with an offered bounty and stated access to identifying information, the timeline for recoveries in hacks can vary widely. Readers should watch for updates that confirm the protocol’s controls are functioning as intended and for any subsequent reporting that clarifies how the cryptographic key exposure occurred and what safeguards have changed.
This article was originally published as Chainflip Confirms $12M Hack, Offers 10% Bounty to Attacker on Crypto Breaking News – your trusted source for crypto news, Bitcoin news, and blockchain updates.
0
0


 Manage all your crypto, NFT and DeFi from one place
Securely connect the portfolio you’re using to start.
 Where will Bitcoin trade next?
Live Polymarket and Kalshi odds on Bitcoin price targets, compared side by side.
See Bitcoin price odds


