
Action Required: Solana Reports Critical Ubuntu Risk for Validators
0
0
Solana infrastructure developer Anza has issued an urgent security warning to mainnet-beta validators running Ubuntu after researchers identified a critical Linux kernel vulnerability that remains unpatched in the distribution. The alert urges affected operators to apply temporary security measures while waiting for an official Ubuntu update.
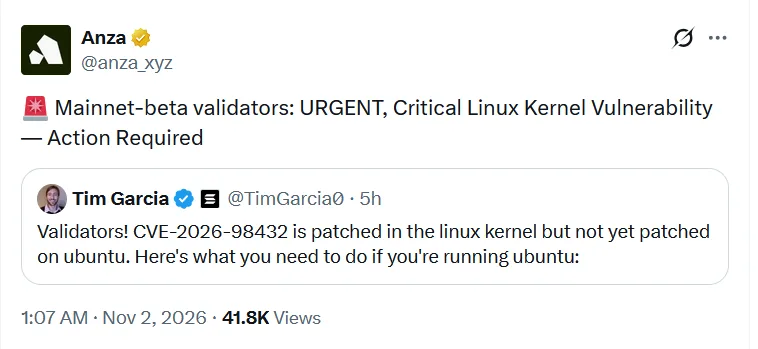
The warning concerns CVE-2026-98432, a use-after-free vulnerability in the Linux kernel’s IPv4 TCP handshake process involving IP options. It carries a CVSS score of 9.8 out of 10, placing it in the critical severity category. Under specific conditions, remote attackers could exploit the flaw without authentication.
Anza Outlines Temporary Fixes for Ubuntu Validators
Anza shared guidance from Tim Garcia, Validator Relations Lead at the Solana Foundation, outlining three temporary security measures for Ubuntu-based validators. The recommendations are designed to reduce exposure until Ubuntu releases an official kernel patch.
The first measure involves using nftables to block incoming TCP packets containing IPv4 options. Validators should also disable Multipath TCP (MPTCP) through sysctl settings and turn off TCP request socket migration.
These measures offer temporary protection rather than a permanent solution, so operators must continue monitoring Ubuntu’s security updates. They should also ensure the firewall rules and system settings remain active after reboots to maintain protection.
Patch Status and Potential Risks
Linux distributions have taken different approaches to addressing the vulnerability, with Debian and Amazon Linux already releasing patched kernels. Ubuntu and Red Hat have yet to provide equivalent fixes, with their security trackers showing that work remains pending or has been deferred.
Despite its critical severity rating, security researchers have noted that exploiting the vulnerability may be more difficult in practice. Demonstrations suggest that an attack could require precise timing and, in some cases, an active MPTCP listener. However, disabling MPTCP alone may not eliminate the risk.
For Solana validators, a successful exploit could compromise the host machine or disrupt network operations. It could also expose sensitive validator identity keys and prevent affected validators from participating in block production.
Anza and the Solana Foundation have urged affected operators to apply the recommended protections without delay. Validators using distributions with available patches should update their kernels and reboot their systems. They should also monitor further security updates, as no active exploitation targeting Solana had been reported at the time of the alert.
The post Action Required: Solana Reports Critical Ubuntu Risk for Validators appeared first on CoinTab News.
0
0

 Manage all your crypto, NFT and DeFi from one place
Securely connect the portfolio you’re using to start.


