Curve Fee Burner Exploit: $38K Stolen, User Funds Remain Safe
0
0
Curve Fee Burner: How Did an Order Check Drain $38K in DAO Revenue?
A small but telling security incident has hit one of DeFi’s best-known protocols.
On November 10, an attacker took roughly $38,200 of DAO revenue from a contract on Ethereum that sells collected protocol earnings.
The Curve fee burner, named CowSwapBurner, had a gap in how it checked orders.
The good news is that no user money was touched, and the protocol moved quickly to shut the weak spot.
This guide explains what happened in plain language, using only the details shared in the project’s official incident thread.
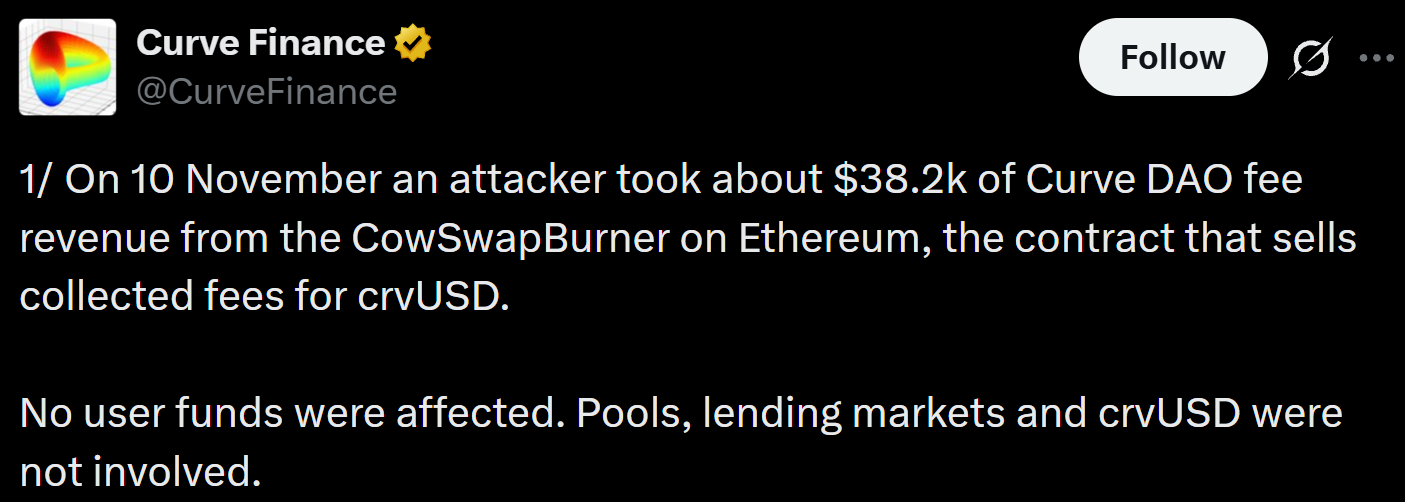
Source: Curve Finance Post
What Happened on November 10
According to the official thread, an attacker took about $38.2K of DAO fee revenue from the CowSwapBurner on Ethereum.
This is the contract that sells collected fees in exchange for crvUSD, the protocol’s stablecoin.
The same post makes one point very clear: user funds were not affected, and pools, lending markets, and crvUSD were not involved.
In simple terms, the protocol collects revenue in many different tokens. A tool like this one turns those scattered balances into a single stablecoin for the treasury, which is controlled by the community that governs the protocol.
When that tool is tricked, the treasury loses income, but the money users have deposited elsewhere stays out of the picture.
| Item | Detail |
| Date | November 10 |
| Network | Ethereum |
| Contract hit | CowSwapBurner |
| Amount taken | About $38.2K (sold for 38,205 USDC) |
| Funds recovered | Not yet |
| User funds affected | None |
How the Curve Fee Burner Exploit Worked
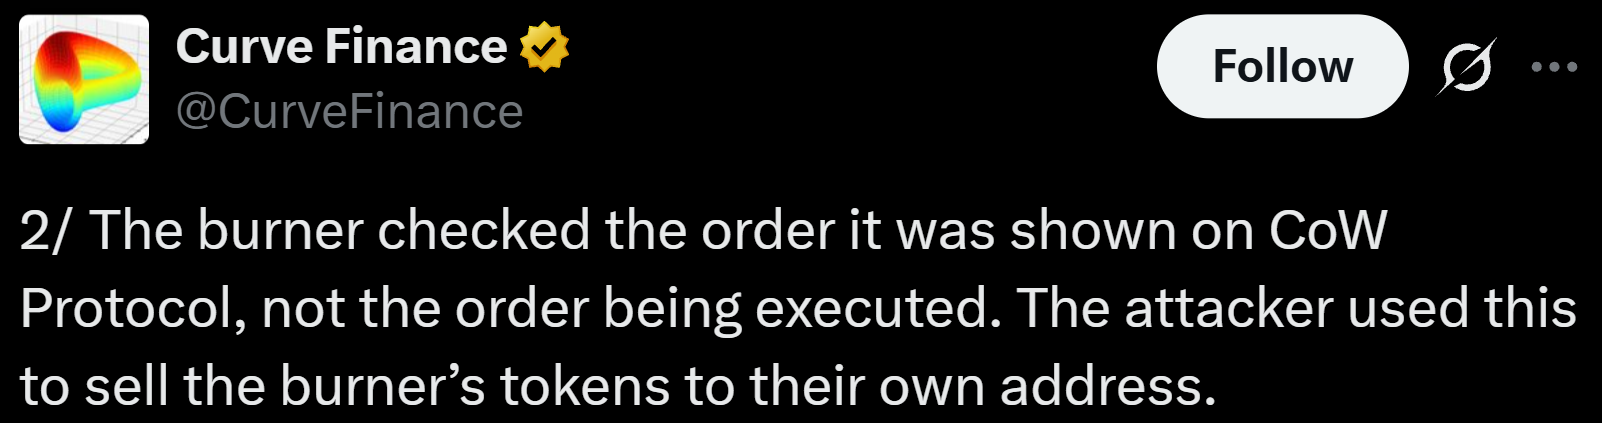
The thread explains the flaw in simple terms: the contract checked the order it was shown on CoW Protocol, not the order that was actually being executed.
Think of a shop assistant who inspects a receipt on the counter but then hands over goods for a different receipt.
The attacker used this mismatch to sell the contract’s tokens to their own address.
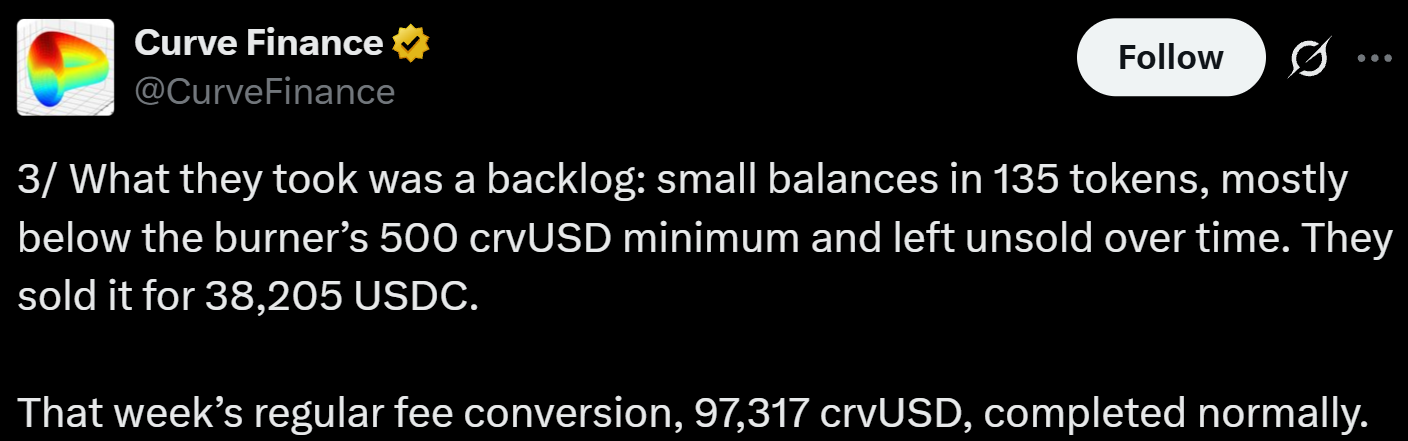
The next post in the thread adds important detail about what was taken:
-
A backlog, not fresh income: the loot was small leftover balances across 135 tokens.
-
Below the minimum: most of these balances sat under the contract’s 500 crvUSD minimum, so they had stayed unsold over time.
-
The result: the attacker sold the backlog for 38,205 USDC.
What Was and Was Not Affected
The project separates the damage from the parts that stayed safe, as the same thread shows.
| Affected | Not affected |
| Backlog of small token balances held in the contract | User funds |
| Ethereum conversion of DAO revenue, now paused | Pools and lending markets |
| – | crvUSD |
| – | That week’s regular conversion of 97,317 crvUSD, which completed normally |
In short, the loss came from leftover dust that had piled up, while the main weekly conversion went through as planned.
This matters because it shows the exploit did not interrupt the protocol’s normal revenue flow that week. It only reached the small balances that had never cleared the minimum.
How the Emergency DAO Responded
The official update says the Emergency DAO disabled the contract at 13:59 UTC the same day. Conversion of revenue on Ethereum is paused for now, although fees keep accruing in the meantime.
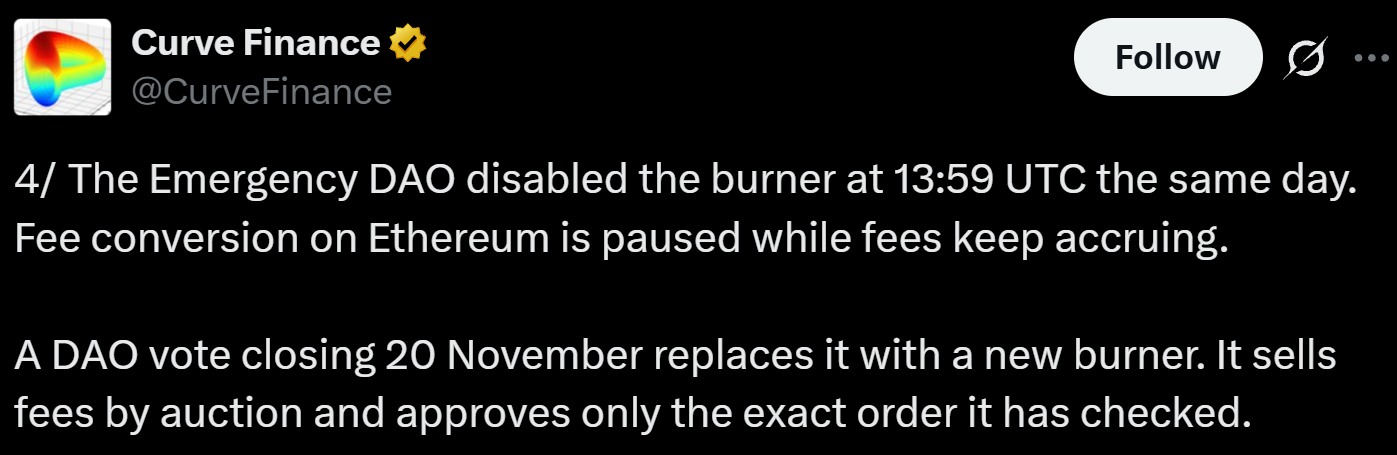
A DAO vote closing on November 20 would replace the old contract with a new Curve fee burner.
According to the thread, the replacement works differently in two ways:
-
It sells fees by auction.
-
It approves only the exact order it has checked.
That second change targets the weakness directly. The old contract looked at one order and executed another; the new design is meant to approve only what it has verified. Until the vote ends, Ethereum conversion stays on hold.
The thread does not state the exact time of the exploit, so the table below lists only the dates and times the project gave.
| When | What happened |
| November 10 | Attacker sells the backlog to their own address |
| November 10, 13:59 UTC | Emergency DAO disables the contract |
| Until the vote ends | Ethereum conversion paused, fees keep accruing |
| November 20 | Vote on the replacement closes |
What Users and Other Teams Should Do
The final post in the thread is short and practical:
-
Everyday users: no action is needed.
-
Teams using a fork of CowSwapBurner: check your own deployment, as the project advises.
-
Recovery: the funds have not been recovered.
-
Takeaway: small leftover balances can add up, and a check only protects you if it confirms the exact order being executed.
For a deeper technical record, the project also published a security disclosure in its incident-reports repository.
Conclusion
This episode shows how even a modest contract can leak value when one check is missing.
The Curve fee burner loss was small, user money stayed safe and the response was quick.
The next step to watch is the DAO vote closing on November 20, which decides whether the improved design goes live.
Disclaimer
This article is for educational and informational purposes only and is not financial or investment advice. Crypto assets are high risk, their prices can be very volatile, and you can lose some or all of your money. Always do your own research and consider speaking with a licensed financial advisor before making investment decisions.
0
0

 Manage all your crypto, NFT and DeFi from one place
Securely connect the portfolio you’re using to start.
 Where will Ethereum trade next?
Live Polymarket and Kalshi odds on Ethereum price targets, compared side by side.
See Ethereum price odds


